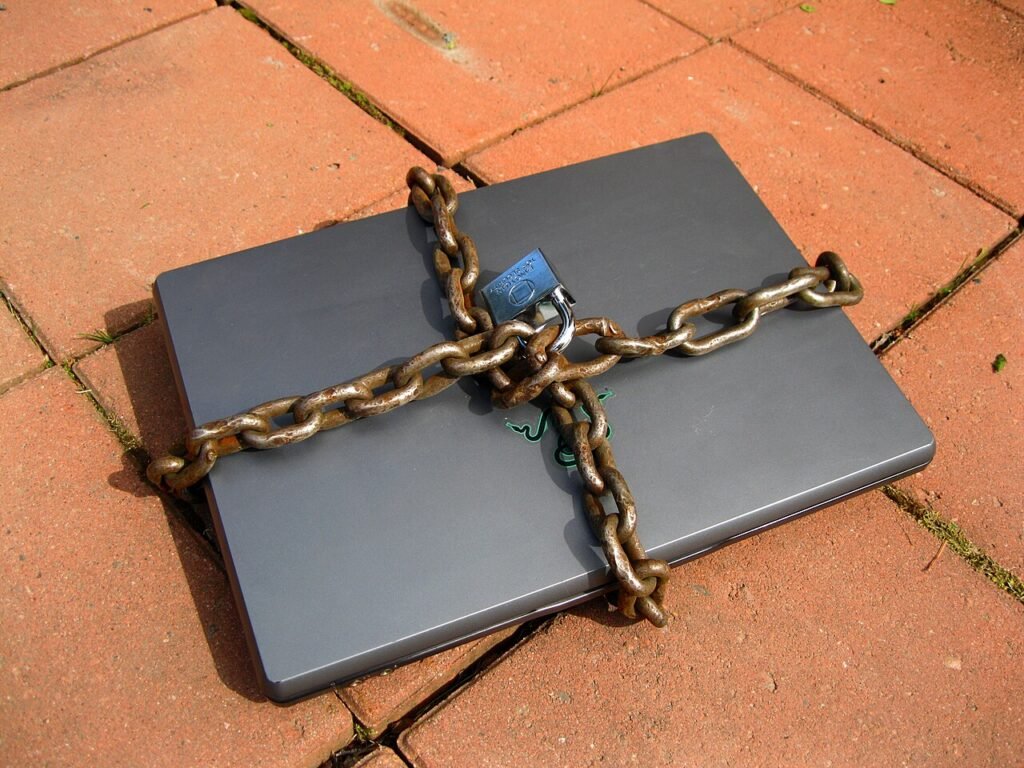
JPMorgan Chase, Visa and Mastercard have all confirmed that third-party companies working for them were hit in a cyberattack, after a ransomware group calling itself “n0n” published customer data stolen from their vendors online. The three financial giants stressed that their own systems were not breached and no card numbers were exposed — but the leak still puts thousands of customers at risk of targeted scams.
The disclosures came on Thursday 19 November, three days after n0n claimed on 16 November that it had obtained data belonging to all three companies. The group gave them 48 hours to pay a ransom, then published the stolen files online once the deadline passed. Researchers who reviewed the datasets say the files contain names, email addresses, phone numbers and partial home addresses — the kind of personal detail fraudsters use to make fake messages look genuine.
What data was leaked in the JPMorgan Visa Mastercard cyberattack
The scale of the leak differs across the three companies, but the pattern is the same: marketing and customer-engagement records held by outside vendors, not core banking or payment systems.
At JPMorgan, a Reuters review of the leaked files found more than 16,000 customer email addresses, some accompanied by phone numbers and postal codes, along with what appear to be 124 email addresses belonging to bank employees. Researchers at the cybersecurity news site Cybernews, who also examined the files, say the affected customers all appear to be holders of the Chase Reserve card, the bank’s invitation-only card for very wealthy clients.
The Visa files hold thousands of purported customer emails, phone numbers and marketing campaign records, mostly from Asia-Pacific markets including Hong Kong, Japan, Singapore, Australia, South Korea, Taiwan, the Philippines, Malaysia and Macau. Cybernews counted more than 6,000 premium cardholders in the Visa data, taken from what looks like a marketing platform for the company’s dining programmes in the region.
The Mastercard leak is smaller, with about 2,000 entries covering customers in North America, the Middle East and Africa who were enrolled in a specific benefit programme, plus a small number of employee email addresses. One Cybernews researcher noted the entries were so jumbled that some may be test data rather than real customer records. None of the three companies has named the vendors that were attacked, and Reuters said it could not independently verify the authenticity of the leaked data.
Who is the n0n ransomware group
The n0n group only emerged in mid-September 2026, but it has grown with remarkable speed. Cyber threat researchers at SocRadar described it as an AI-powered extortion racket that had already infiltrated at least 93 organisations across 18 countries, with total ransom demands of $283.7 million. The group has now claimed roughly 200 victims, according to the cybercrime research platform eCrime.ch, and last week it claimed an attack on the travel company Expedia. The attacks reportedly rely on weak or stolen login credentials rather than software vulnerabilities — a reminder that even the world’s biggest financial firms can be exposed through the smaller companies in their supply chain.
What the three companies said
JPMorgan said in a post on X on Thursday that some of the companies providing services to the bank had been hit by a cyberattack. “Based on our investigation so far, we believe the attackers accessed certain marketing data held by those vendors, which may include some customer names and email addresses. There is no disruption to our services,” the bank said. It added that it would contact affected customers directly and offer support, including complimentary credit monitoring where appropriate.
Visa said the claims were “associated with an incident involving a third-party service provider in Asia Pacific. Visa’s systems were not involved and were not impacted. No payments data such as card numbers were affected.” Mastercard said it was recently informed of an incident “at a third-party provider that resulted in the exposure of limited amount of email addresses — non-payments information — from a small subset of cardholders enrolled in a specific benefit program. There is no impact to the Mastercard payment network or the ability for people to use their cards.”
JPMorgan was also quick to separate the cyberattack from a separate problem earlier in the week, when Chase customers saw slow transactions. “There is no connection to service disruption of some customers experienced earlier this week,” a bank spokesperson said — the earlier outage stemmed from a software bug. Visa echoed the point, saying its vendor breach was unrelated to the system disruptions seen across different industries this past week.
No card numbers exposed — but phishing risk remains
The reassuring part of the story is what was not stolen. No card numbers, security codes or other payment data were exposed, and all three companies say their payment networks and core systems are unaffected. Customers can still use their cards normally.
The danger now is what criminals can do with the leaked details. Security analysts warn that names, contact details and bank affiliations give scammers credible material to launch targeted phishing campaigns — messages that appear to come from a person’s own bank or card company and trick them into handing over passwords, one-time codes or money. The fact that the leaked data includes high-net-worth Chase Reserve customers makes those targets especially attractive to fraudsters.
Anyone who banks with JPMorgan Chase or holds a Visa or Mastercard should treat unexpected messages with extra care in the coming weeks. Do not click links or download attachments in emails or text messages claiming to be from your bank or card company, and never share passwords or one-time codes. Instead, contact your bank through its official app or the number printed on the back of your card. Check account statements regularly, and switch on two-factor authentication wherever it is offered. JPMorgan says it will contact affected customers directly — if you receive such a message, verify it through an official channel before acting on it. The incident is the latest reminder that in modern finance, security is only as strong as the weakest link in the chain. The banks themselves were not breached — but the vendors holding their customers’ marketing data were, and that was enough to put thousands of people’s personal details on the dark web.
Related Posts
 TechnologyKarachi Safe City Phase-II: Sindh Cabinet Approves Rs5.766 Billion for 2,300 AI Cameras
 TechnologyPTA Approves Advanced Firewall to Strengthen Social Media Monitoring in Pakistan
 TechnologyUfone and Telenor Partner with Xiaomi to Bring Redmi 17 5G with Bundled Data Plans
 TechnologyVGO TEL Tops Pakistan’s Local Mobile Phone Assembly in 2026 With 3.5 Million Handsets
 TechnologyAlibaba DigiSME Reaches 2,000 Pakistani SMEs in 100 Days as Export Orders Grow
 TechnologyNADRA Extends Digital Nikah Registration to Islamabad and Quetta via PakID
Most Popular
 How-ToPTA Tax Calculator 2026: Check Mobile Tax on Any Phone421 views
 Pakistan NewsPIA Boeing 787 Lease Deal: What It Means for the Airline396 views
 Canada JobsTech Jobs in Canada: Roles, Salaries, and Skills Needed392 views
 SportsUEFA Champions League 2026-27: Format, Teams and Schedule390 views
 TechnologyPM Shehbaz Sets November Deadline for Alibaba AI and Digitalisation Projects in Pakistan370 views
 ShowbizWomen’s Fashion in Pakistan 2026: Trends, Brands and Style Guide366 views